Security and confidentiality
We may hold your bank access, your payroll and your employees' information. Here is how we handle it.
A firm that works inside your business can see banking, payroll, benefits, credit cards, vendor records and financial statements. The controls below are the ones actually in place. Nothing here is aspirational.
Named, role-based access
Every engagement lists who has access to what. View-only wherever possible.
Multi-factor authentication
On every system that supports it, tied to individual people, never a shared phone.
Credentials in a business password manager
Never shared by text or email. Revoked the day someone leaves an engagement.
Documents through a secure client portal
Not email attachments.
Read-only bank feeds
We never move money without your written approval, one payment at a time.
Firm-controlled devices
Client information lives on managed workstations, not personal phones.
An annual access review
Who has access to what, checked once a year and after any staff change.
Confidentiality in writing
A confidentiality agreement with every client. We'll sign yours.
What we don't claim
We don't hold a SOC 2 report and we won't describe anything here as "bank-level security." If a formal certification becomes part of how we work, it will be named on this page with its date. Until then, the controls above are the claim.
If something looks wrong
Call Chris directly at 630-643-5600. A suspicious email that appears to come from us, a payment request you didn't expect, a login you don't recognize: we'd rather hear about it in the first hour than the first week. We never ask for credentials by email or text.
Tell us what's going on. We'll tell you what we see
One conversation with Chris, no deck. He'll tell you what he sees and what it would take to fix it, including if the answer is that you don't need a CFO yet.
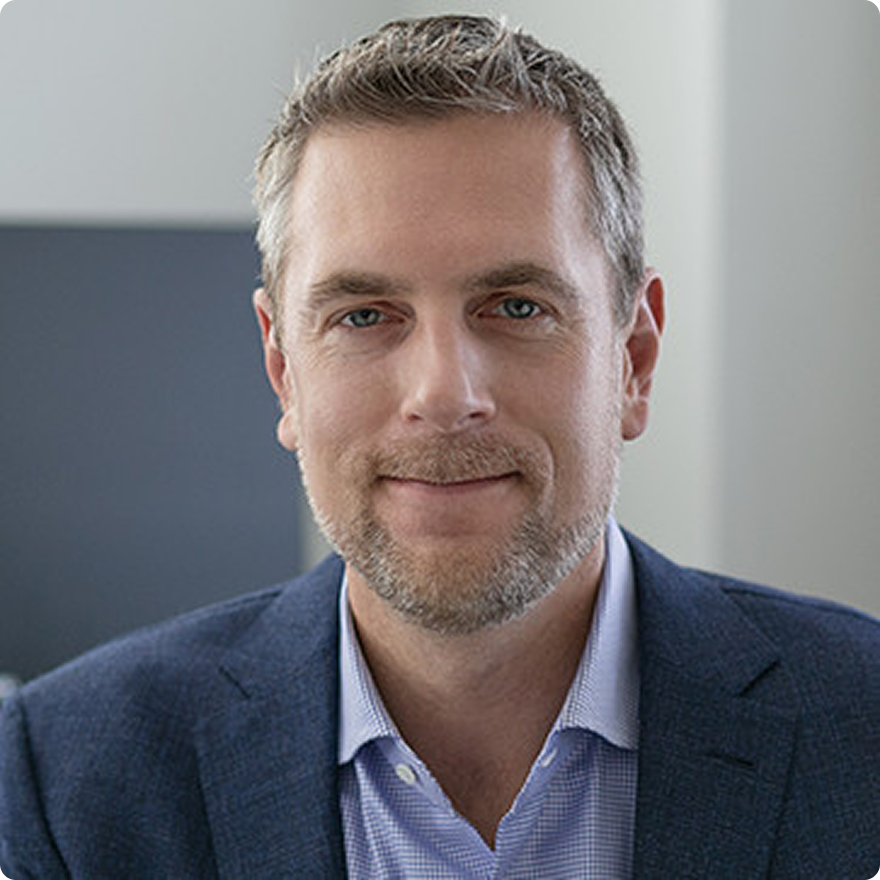
Chris Greco, Founder and President.
Your first call is with him, not a sales team.